
Fake Ledger App Steals $9.5 Million After Passing Apple Review
For those of us living in the tech-saturated corridors of Seattle, from the glass towers of South Lake Union to the creative hubs in Capitol Hill, there is a pervasive belief that we are “digitally literate” enough to avoid the obvious traps. We trust the ecosystems we live in, especially when those ecosystems are curated by giants like Apple. But a recent security breach has proven that even the most stringent gatekeepers can fail, leaving a trail of financial devastation that hits home for the city’s significant community of early adopters and cryptocurrency investors.
Between April 7 and April 13, 2026, a malicious clone of the Ledger Live app managed to bypass Apple’s app review process and land directly in the Mac App Store. For about two weeks, this fake application sat there, masquerading as a legitimate tool for managing crypto assets. The result was a catastrophic drain of approximately $9.5 million from more than 50 victims. For many, this wasn’t just a loss of “play money”—it was the disappearance of entire retirement funds and decade-long savings, wiped out in a matter of seconds.
The Anatomy of a High-Stakes Phishing Campaign
The sophistication of this scam didn’t lie in complex coding, but in the exploitation of trust. The fake app was submitted under the publisher name ‘Leva Heal Limited,’ an entity with no connection to the actual Ledger development team. To create a facade of legitimacy and activity, the attackers employed a rapid-fire update strategy, pushing the app from version 1.0 to 5.0 within a mere two-week window. This fake version history likely tricked users into thinking the app was being actively maintained and improved.
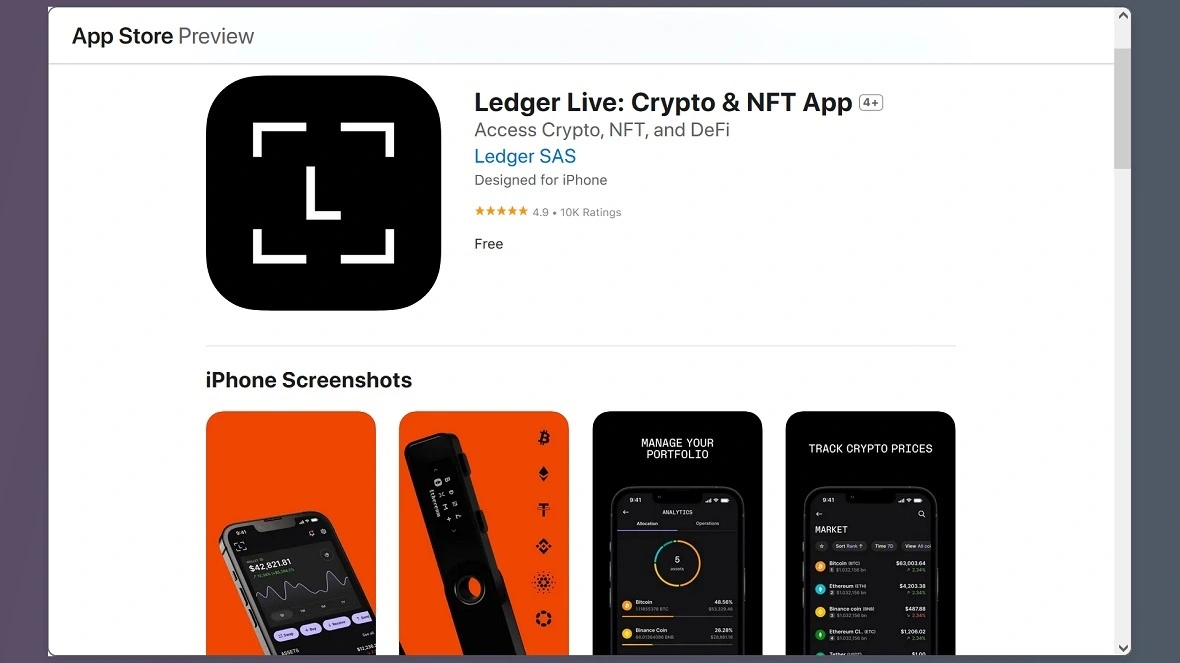
The trap was sprung the moment a user attempted to set up their wallet. Unlike the legitimate Ledger Live app—which is distributed exclusively via the official Ledger website and never through the Mac App Store—this clone prompted users to enter their seed phrases. In the world of cryptocurrency, the seed phrase is the master key; anyone who possesses it has total control over the assets. By entering these recovery phrases into the malicious app, victims unknowingly handed the keys to their digital vaults directly to the attackers.
The scale of the theft was staggering. Blockchain investigator ZachXBT, who uncovered the scope of the operation, identified that the funds were siphoned across multiple blockchains, including Bitcoin, Ethereum, Solana, Tron, and XRP. Whereas many lost significant sums, three specific victims suffered seven-figure losses, with individual thefts reaching $3.23 million, $2.08 million, and $1.95 million between April 8 and April 11. Even well-known figures weren’t immune; musician G. Love reported the loss of 5.9 BTC (valued at roughly $430,000) after downloading the app while configuring a new computer.
Following the Digital Breadcrumbs to KuCoin
Once the assets were stolen, the attackers didn’t simply hold them. They utilized a sophisticated laundering pipeline to obscure the trail. The stolen funds were routed through a series of transactions and eventually landed in deposit addresses on the KuCoin crypto exchange. To further mask the origin of the money, the hackers employed a centralized mixing service known as AudiA6. This service specializes in laundering cryptocurrency in exchange for high fees, making it significantly harder for law enforcement and investigators to trace the funds back to a specific individual.
This incident raises harrowing questions about the reliability of centralized app stores. When a user downloads an app from the Mac App Store, there is an implicit assumption that Apple has vetted the software for basic security and authenticity. The fact that a blatant phishing tool could remain live for two weeks suggests a critical failure in the review process. While Apple has since removed the app, they have yet to provide a detailed explanation of how ‘Leva Heal Limited’ managed to slip through the cracks. This gap in security has led some, including ZachXBT, to suggest that Apple could potentially face class-action lawsuits given the sheer volume of capital lost.
For those in the Pacific Northwest, where the intersection of finance and technology is so dense, this serves as a stark reminder to implement security best practices regardless of where a piece of software originates. The reliance on “official” stores is no longer a foolproof strategy for asset protection.
Navigating the Aftermath in the Seattle Area
If you or someone you know in the Seattle metro area has fallen victim to this or similar phishing schemes, the window for action is often very small. As cryptocurrency transactions are immutable, recovery is incredibly difficult, but not impossible if the right professional channels are engaged immediately. Given my background in analyzing these macro-trends, I recommend that residents of the Puget Sound region appear toward specific types of local expertise to mitigate the damage and report the crime.
When seeking help, avoid “recovery agents” found on social media, as these are almost always secondary scams. Instead, focus on these three professional archetypes:
- Forensic Blockchain Analysts
- Look for specialists who can provide documented evidence of fund movement. You need a professional who can generate a comprehensive report of the flow of assets from your wallet to exchanges like KuCoin. This documentation is essential when filing reports with the Federal Trade Commission (FTC) or the Securities and Exchange Commission (SEC).
- Consumer Protection Attorneys
- Seek out law firms in the downtown Seattle area that specialize in digital assets and consumer fraud. Specifically, look for attorneys who have experience dealing with platform liability and the Washington State Attorney General’s Office. They can advise on whether you have grounds for a claim against the platform that allowed the malicious software to be distributed.
- Crypto-Specialized CPAs
- A loss of this magnitude has significant tax implications. You need a Certified Public Accountant who understands the nuances of “theft loss” deductions for digital assets under current IRS guidelines. Ensure they have a track record of handling high-net-worth crypto portfolios to ensure your losses are recorded correctly for future tax filings.
The loss of millions of dollars in a single week highlights a dangerous evolution in phishing: the move from sketchy emails to “verified” app stores. As we continue to integrate digital assets into our financial lives, the burden of verification remains with the user. Always verify the distribution channel—if a company like Ledger says they don’t use the App Store, believe them over the convenience of a “Receive” button.
Ready to find trusted professionals? Browse our complete directory of top-rated cybersecurity experts in the seattle area today.