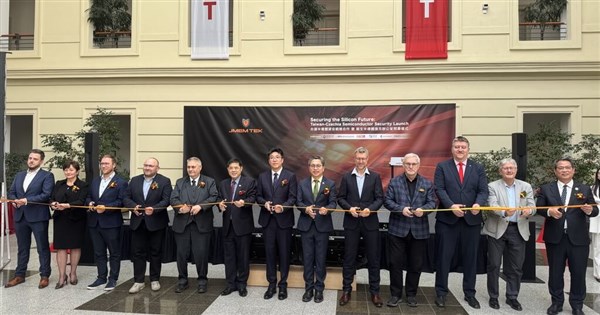
Jmem Technology Opens Semiconductor Cybersecurity Office in Brno
When I first saw the headline about Jmem Technology opening a new office in Brno, my initial thought wasn’t about Central Europe—it was about the quiet hum of servers in a data center off Route 1 in Austin, Texas. That’s because what’s happening in Taiwan’s semiconductor supply chain isn’t just a geo-political footnote; it’s a direct current running through the veins of our own tech ecosystem here in the Hill Country. Jmem, a firm specializing in hardening chip design against cyber intrusions, isn’t just expanding its footprint—it’s signaling a shift in how the world’s most critical silicon is being defended. And for Austin, a city that’s staked its future on being more than just a live music capital but a legitimate contender in the global semiconductor fray, that shift has very real, very local implications.
Let’s unpack why this matters to someone checking their email at a co-working space on East 6th Street or overseeing a fab line in Northeast Austin. Jmem’s core function—providing cybersecurity solutions specifically for semiconductor intellectual property—addresses a vulnerability that’s become terrifyingly obvious in recent years. We’ve seen how easily a single point of failure in chip design can cascade: from the 2020 SolarWinds hack exposing supply chain fragility, to the more recent, targeted efforts to steal or sabotage advanced node designs. Jmem doesn’t build firewalls for networks; they build them into the very architecture of the chip, using techniques like logic locking and camouflaging to make reverse engineering or tampering exponentially harder, even if someone gets physical access to the design files. Their move to establish a European hub in Brno—a city with deep ties to engineering talent through Masaryk University and a growing reputation as a Central European tech hub—isn’t just about proximity to European clients. It’s about creating redundancy, ensuring that if geopolitical tensions disrupt operations in Taiwan, their critical IP protection services can continue uninterrupted. For Austin, this underscores a truth we’ve been living: our role in the semiconductor ecosystem isn’t just about manufacturing wafers; it’s about securing the entire stack, from EDA tools to IP cores.
This connects directly to Austin’s own semiconductor ambitions. The city isn’t just passively benefiting from the CHIPS Act; it’s actively positioning itself. Consider the University of Texas at Austin’s Cockrell School of Engineering, which has long been a powerhouse in microelectronics research, or the SEMATECH consortium’s historical roots here that helped establish Austin as an early epicenter of semiconductor R&D. More recently, Samsung’s massive Taylor expansion—just 30 minutes northeast of downtown—represents a $17 billion bet on advanced node production. But with that scale comes heightened risk. A facility like Samsung Austin isn’t just making chips; it’s producing some of the most advanced, valuable IP on the planet—making it a prime target for state-sponsored espionage or cybercriminal groups looking to exploit design flaws. Jmem’s expansion highlights that the conversation in Austin can’t stop at fab yield rates or job creation numbers; it has to include the often-invisible layer of hardware-level security. It’s why entities like the Texas Advanced Computing Center (TACC) at UT, which partners with semiconductor firms on simulation and security research, are becoming increasingly vital. Or why the Greater Austin Chamber of Commerce’s semiconductor initiative is now quietly emphasizing supply chain resilience alongside economic development metrics.
There’s as well a second-order effect worth considering: the talent implication. As semiconductor firms double down on securing their IP, the demand for engineers who understand both VLSI design and cybersecurity isn’t just growing—it’s bifurcating. We’re seeing the emergence of a hybrid role: the hardware security specialist. This isn’t someone who just configures firewalls; it’s an engineer who understands transistor-level layouts, can spot a side-channel vulnerability in a power analysis trace, and knows how to implement obfuscation techniques during the GDSII streamout process. In Austin, this means opportunities not just at the massive fabs, but also at specialized firms and research labs. Think about the talent pipeline: UT’s electrical and computer engineering department offers courses in hardware security, and organizations like the Austin Technology Incubator (ATiC) have started to see spin-offs focused on exactly this niche. For professionals in Austin looking to future-proof their careers—or for companies struggling to find this rare skill set—it’s a signal that investing in cross-disciplinary training isn’t just nice to have; it’s becoming table stakes.
Given my background in analyzing how global tech trends reshape local economies and workforce demands, if this trend toward hardware-level security impacts you in Austin—whether you’re an engineer at a fab, a startup founder building IP, or a city planner thinking about long-term economic resilience—here are the three types of local professionals you need to know about:
- Hardware Security-Focused ASIC Design Consultants: Look for firms or individuals who don’t just do standard RTL-to-GDSII flows but explicitly integrate security hardening steps—like logic locking, camouflaging, or entropy sources—into their design process. They should be able to reference specific standards (like those from the IEEE Computer Society’s Hardware Security Technical Committee) and demonstrate experience with tools from vendors like Synopsys or Cadence that have security-specific features. Ask for case studies involving IP protection, not just network security.
- Semiconductor Supply Chain Risk Analysts with Local Government Ties: These professionals bridge the technical and the policy. Seek out experts who understand both the technical nuances of semiconductor vulnerabilities (like those exploited in fault injection attacks) and the landscape of federal and state incentives (CHIPS Act, Texas Semiconductor Initiative). Ideal candidates often have backgrounds in places like the Texas Military Department’s cybersecurity unit or have worked with entities like the National Security Collaboration Center (NSCC) in San Antonio, which focuses on securing critical infrastructure. They should help you map your specific exposure points—not just hypothetically, but in relation to actual threat actors targeting the Austin semiconductor corridor.
- Technology Transfer & IP Strategy Attorneys Specializing in Hardware: Standard IP lawyers won’t cut it here. You need counsel who understands that protecting a chip design isn’t just about filing patents—it’s about trade secret strategy, managing access to GDSII files, and navigating export controls (like EAR) that now explicitly cover certain cybersecurity technologies for semiconductors. Look for attorneys who regularly work with UT’s Office of Technology Commercialization or who have advised clients involved in SEMATECH-aligned consortia. Their value lies in helping you structure not just protection, but also secure collaboration—vital in an era where innovation often happens across institutional boundaries.
Ready to find trusted professionals? Browse our complete directory of top-rated experts in the Austin area today.