FBI Warns: Russian Hackers Targeting Signal & WhatsApp Users in Phishing Attacks
The FBI has publicly attributed ongoing phishing campaigns targeting users of encrypted messaging apps like Signal and WhatsApp to Russian intelligence services. This marks the first time the agency has directly linked these attacks to a specific nation-state actor, escalating concerns about the security of private communications for individuals considered valuable intelligence targets. The campaigns, which have already compromised thousands of accounts globally, aim to bypass end-to-end encryption not by breaking it, but by hijacking accounts and gaining unauthorized access to sensitive data.
How the Attacks Work: Account Hijacking, Not Encryption Breaking
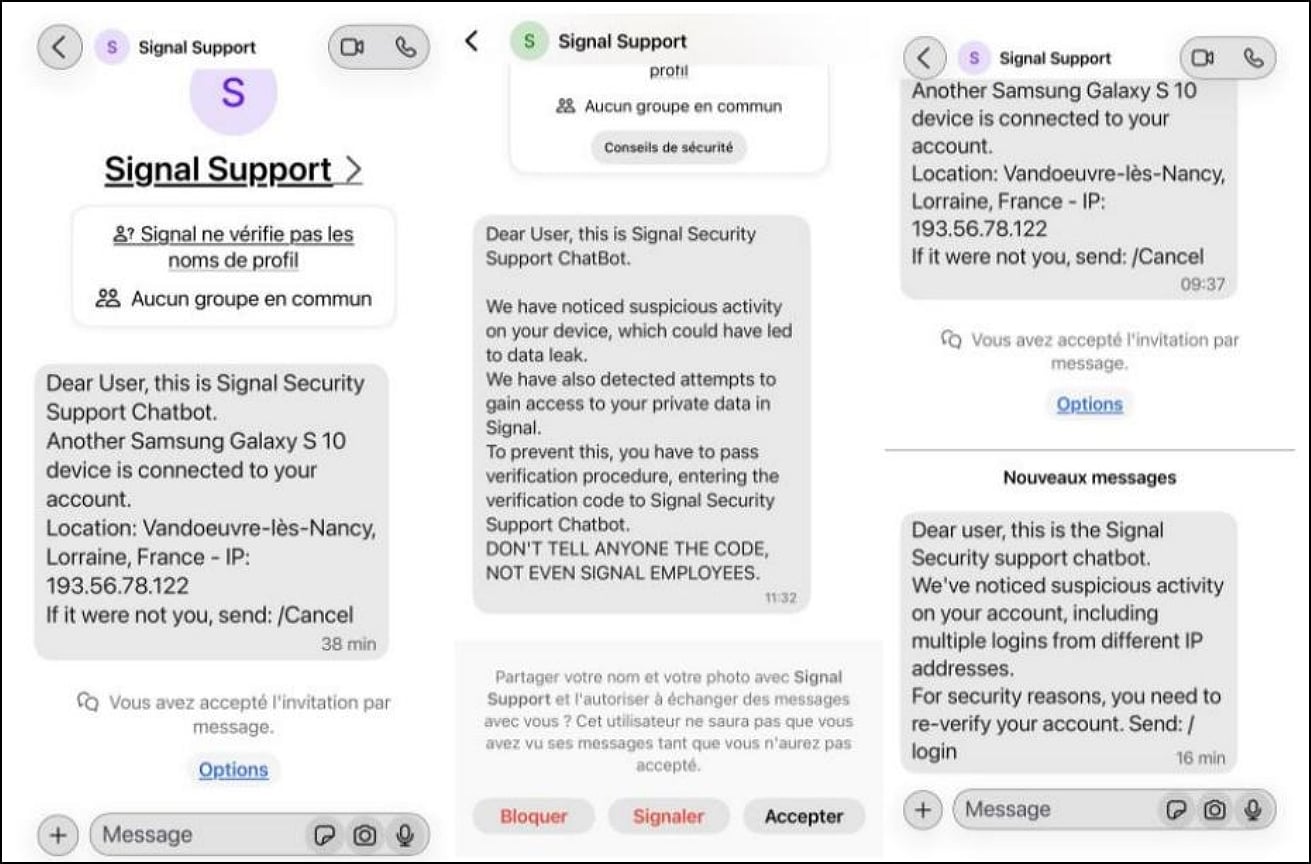
Crucially, the FBI emphasizes that the encryption within Signal, WhatsApp, and similar platforms remains secure. The attacks aren’t exploiting vulnerabilities in the encryption itself. Instead, threat actors are focused on account takeovers. The primary method involves phishing messages that impersonate support accounts, tricking users into performing actions that grant attackers access. These actions often include sharing verification codes or scanning malicious QR codes that link accounts to attacker-controlled devices. Signal’s documentation on linked devices explains the process attackers are exploiting.
Similar tactics were previously flagged by Dutch and French cybersecurity authorities. France’s Cyber Crisis Coordination Center (C4) published an alert detailing the widespread nature of these attacks across multiple countries. The advisories consistently point to the same technique: bypassing encryption through account hijacking or linking devices.
Source: FBI
Who is Targeted and What’s at Risk?
The FBI’s public service announcement specifically identifies targets as “individuals of high intelligence value,” including current and former U.S. Government officials, military personnel, political figures, and journalists. Once access is gained, attackers can read private messages, access contact lists, impersonate victims, and launch further phishing campaigns, leveraging the compromised accounts as trusted sources. This creates a cascading effect, potentially expanding the reach of the attacks significantly. The FBI reports that “thousands” of accounts have already been affected worldwide.
The risk extends beyond the immediate compromise of messages. Attackers can silently monitor communications, join group chats, and send messages as the compromised user, making detection difficult. This ability to operate undetected allows for prolonged surveillance and the potential for disinformation campaigns. The compromised accounts can likewise be used to gather further intelligence or to gain access to other systems and networks.
The Broader Context: State-Sponsored Phishing Campaigns
While the FBI’s recent attribution is new, state-sponsored phishing campaigns are not. Nation-state actors have long employed phishing tactics to gather intelligence and conduct espionage. The focus on encrypted messaging apps reflects the increasing use of these platforms by individuals who require secure communication. The shift towards targeting CMAs demonstrates an adaptation to evolving security practices and a recognition of the challenges in intercepting encrypted communications directly. The Hill reported on the FBI Director Kash Patel’s statement regarding the ongoing nature of these campaigns.
Why Account Linking is a Key Vulnerability
The success of these attacks hinges on exploiting features designed for convenience – specifically, the ability to link accounts to multiple devices. Both Signal and WhatsApp allow users to link their accounts to desktop or web applications by scanning a QR code. Attackers are leveraging this functionality to gain access by tricking users into scanning malicious codes, effectively adding the attacker’s device to the victim’s account. This allows the attacker to receive messages and potentially take control of the account without requiring the victim’s primary authentication credentials.
Source: France’s Cyber Crisis Coordination Center (C4)
Mitigation and What to Do Now
The FBI, CISA, and cybersecurity authorities are urging users to remain vigilant and adopt cautious practices. Key recommendations include:
- Be suspicious of unexpected messages: Exercise caution with any unsolicited messages, even if they appear to reach from a trusted source.
- Never share verification codes: Do not share verification codes with anyone, including those claiming to be platform support personnel.
- Be wary of QR codes: Avoid scanning QR codes from unknown or untrusted sources.
- Review linked devices: Regularly review the list of linked devices in your Signal and WhatsApp settings and remove any unfamiliar or unauthorized devices.
The Internet Crime Complaint Center (IC3) provides additional resources and guidance on reporting phishing attempts and protecting against cyber threats.
Looking Ahead: Continued Vigilance and Platform Responses
The FBI and CISA are continuing to investigate these attacks and work with Signal and WhatsApp to enhance security measures. Users should expect ongoing advisories and updates as the situation evolves. The incident underscores the importance of multi-factor authentication and a healthy skepticism towards unsolicited communications, even within seemingly secure messaging environments. The focus will likely shift towards improving user awareness and strengthening account recovery processes to prevent unauthorized access. Further investigation may reveal the full scope of the compromised data and the ultimate objectives of the Russian intelligence services behind these campaigns.